No AI policy yet? Your first 30 days of managing shadow AI
Meeting bots, browser extensions and AI features in software you already pay for: how to find them and take control in a month.
Read the article
Plain-English writing on managed IT and cyber security from the team that runs it day to day.
A week-by-week October plan that turns staff awareness into four practical, positive habits.
A forgotten recording can send your post-call debrief to the client you were discussing.
Two questions decide whether a process is ready to automate, and most of the work is never the tool.
How to turn scattered IT spend into a predictable twelve-month plan, from support and licences to the laptop replacement cycle.
A practical order of work for wholesalers: verification first, then email and identity, then the warehouse network, then recovery.
Why forced complexity made passwords worse, what a password manager actually changes, and the one attack it will never stop.
The technology is rarely the hard part of an AI project. Permissions, logging and who checks the output are.
Microsoft is retiring the six digit codes it sends by text and phone call. Here are the four dates, and how to move your team across without a queue at the front desk on a Monday morning.
Voice calls, texts, QR codes and Teams messages bypass every control you bought for your inbox. What to do about the other channels.
The work behind the term, and five signs a business has outgrown ringing someone when things break.
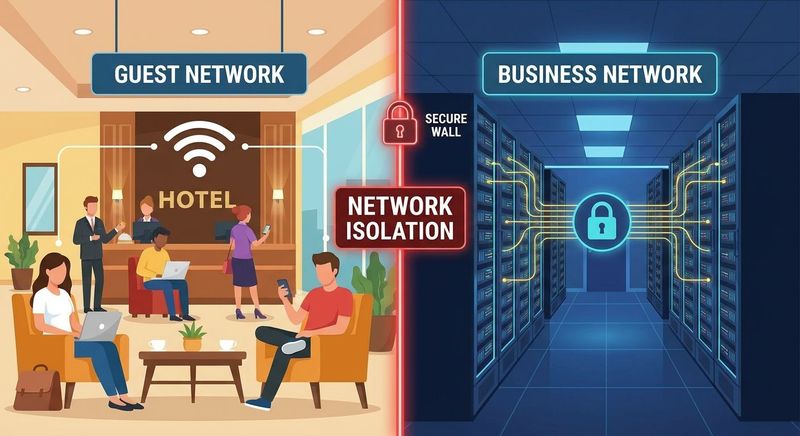
A separate Wi-Fi name is not a separate network. What guest Wi-Fi separation takes in a practice, a hotel or an office, and how to check yours.
A practical rollout order for passkeys and conditional access, from the pilot group through to blocking legacy sign-ins.
Offboarding done properly: session revocation, mailbox conversion, file ownership, and the forgotten logins that outlive the person who set them up.
The signs of a compromised business mailbox, the controls that close the common routes in, and the seven steps that belong in your first hour.
A plain-English look at DORA: who it covers, what it demands, and where accountancy and financial-services firms in Ireland fit in.
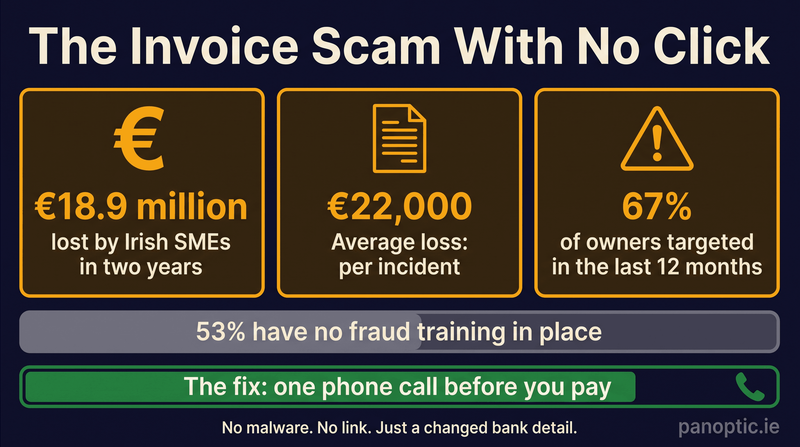
How invoice redirection and CEO impersonation scams beat spam filters and antivirus, and the phone-call habit that catches them before the transfer goes through.
Shadow AI in Irish SMBs: what the law already requires of you, and the six controls that keep client data out of a chat window.
Ransomware attacks cost Irish SMBs an average of €220,000 per incident. Learn the practical steps to protect your business with patching, offline backups and endpoint protection.
Modern cyber resilience depends on separating trusted systems, guest access, and critical business devices on the network.
The portals, line-of-business apps and logins your team depends on hold a lot of trust — and a lot of data. Here's what testing them looks at.
When the line drops, the business stops. Business-grade gateways and automatic failover keep you online when a connection or device fails.
Laptops, phones and servers don't look after themselves. Managed devices are set up the same way every time, kept patched and watched — so ransomware is boxed in the moment it lands.
A deleted file or a compromised mailbox shouldn't cost more than a few minutes. Independent backup of Microsoft 365 and your files makes recovery quick — and provable.
External attack-surface testing looks at your business the way an outsider would — what's reachable from the public internet, and where the soft spots are.
Getting in is only step one. Internal testing measures how far an intruder could move once they have a foothold on your network.
It's hard to plan when you can't see where you are. Regular alignment audits measure your setup against best practice, with prioritised findings.
Technology that's only dealt with when it breaks always feels like firefighting. A rolling roadmap keeps decisions planned, not panicked.
Choosing the wrong tool is expensive twice — once to buy it, and again to switch away. Independent guidance helps you get the right fit first time.
Microsoft 365 and Azure are where a lot of business now lives — and their default settings are rarely the safest. A cloud security review surfaces what's quietly exposed.
A network you can't see is a network you can't fix quickly. Bringing every device onto one dashboard makes faults quick to find and quick to fix.
Adding a floor, a unit or a whole new site shouldn't mean starting again. A network designed with headroom extends cleanly as you grow.
Most breaches start with a person, not a server. A simulated phishing exercise shows whether realistic approaches can fool your team — and turns the result into training.
Wi-Fi that drops in the back office usually comes down to guesswork at install time. Designing from a proper site survey puts coverage where it's actually needed.
The framework the NCSC points to for NIS2: the six functions, the three assurance levels, and a step-by-step run through the free self-assessment.
Navigate the 2025 NIS2 compliance rules for Irish SMEs. Understand the risks, protect your business, and ensure you are prepared with an expert partner.
Discover the benefits of continuous monitoring in cyber security and how it strengthens your business's ability to detect threats and protect sensitive data.
The essential strategies Irish businesses need in 2025 to prevent a ransomware attack, and recover fast if one gets through.
Cyber security starts at the top. How business leaders set the tone that turns staff into a strong first line of defence.
What vulnerability scanning is, how it finds weaknesses before attackers do, and why regular scans are a smart investment.
Book a discovery call and we'll look at your setup, find the gaps, and point you to the services that fit. We keep it plain, and there is no obligation to sign anything.